
Editorial Financial Security Institute's Breached 'Security Watchman,' Redesign Defense System from Scratch
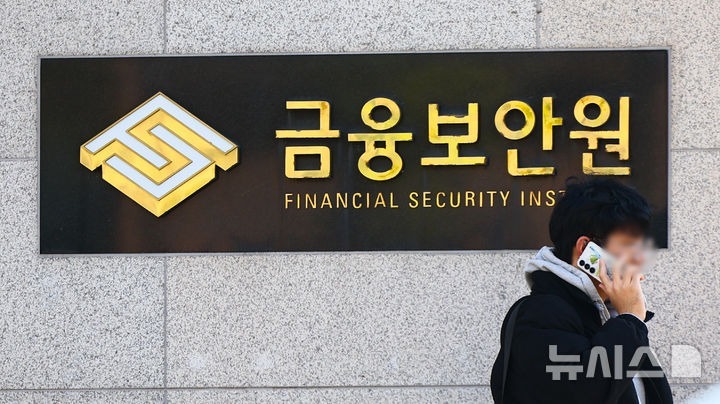
The internal network of the Financial Security Institute, which is solely responsible for information protection in South Korea's financial sector, has been breached by hacking attacks. The control tower that should assess and guide financial companies' security status has failed to protect even its own perimeter, allowing attackers to launch an ambush.
The Financial Security Institute has even canceled the 'Financial Information Protection Conference (FISCON) 2026' scheduled for the 12th, resulting in disruption. Given that even the last bastion of financial security has been shaken, the shock and loss of trust inflicted by this information leak on the entire financial market is truly severe.
Continuous evaluation system breached by spoofed regulator account, the foundation of trust crumbles
The 'Information Protection Continuous Evaluation Support System' where the damage occurred is a channel through which financial companies submit detailed forms and user information to prove their security management systems. Hackers created fake accounts impersonating the Financial Supervisory Service and illegally accessed and stole approximately 850 administrative forms and personal information.
While sensitive information such as customer system configurations reportedly escaped leakage, the very fact that fake accounts impersonating a superior regulatory authority were not filtered out and data extraction was left unchecked has made it impossible to restore market skepticism about the financial security infrastructure.
Complacent authority management and detection failure, a foreseen dereliction of duty
The most painful aspect of this crisis is that not only the technical defense network of external intrusion prevention, but also the basic authentication system for verifying user identity and access authority has been rendered powerless. Before pointing out the security failures of others' houses, the institute should have first strengthened its own internal account issuance and anomalous traffic detection systems.
The fact that real-time detection and blocking did not operate while spoofed accounts downloaded large amounts of data demonstrates that existing defense measures were virtually useless. If a security-specialized agency is this lax, how could any financial company confidently submit its critical security materials in the future?
Must abolish 'fortress model' and transition entirely to Zero Trust system
The government and financial authorities must not treat this catastrophe as a one-time accident and resort to post-hoc remedial measures. They must completely shift the paradigm away from the typical 'fortress model'—layering external defenses while unconditionally trusting internal access—to a 'Zero Trust' defense system that continuously doubts and verifies even logged-in accounts.
Through police investigations, the routes of fake account creation and authority abuse must be clarified unequivocally, and the entire financial sector's access control and data extraction detection systems must be fundamentally redesigned. To protect financial security with national assets at stake, the watchman's personnel and technological renewal is urgent.

Loading comments…